Be ready when a customer, auditor, or board asks how you govern AI
Fractional and project-based AI governance and security leadership for organizations of any size and stage. Founded by a 20+ year former Fortune 100 leader, with that program-building experience scaled to fit.
Confidential by default. A mutual NDA is available before you share anything.
Credentials
We work with growth-stage and mid-market companies, regulated and customer-facing organizations, private equity portfolio companies, and public-sector contractors.
Why this is being asked
employees are regular AI users on corporate devices, up from 15 of 100 a year earlier.
Source: Verizon, 2026 Data Breach Investigations Report
of those users reach AI services through non-corporate accounts on those devices.
Source: Verizon, 2026 Data Breach Investigations Report
of breaches involved a third party, up 60% in a year.
Source: Verizon, 2026 Data Breach Investigations Report
Banning AI does not work. A usable approval path, clear data rules, and an owner for each AI system do.
One program, not six checklists
Most organizations meet each framework on its own, with separate owners, separate evidence, and separate answers to the same questions. We map them once into a single control set, so every audience gets a consistent, defensible answer.
The frameworks
Who asks
What we do
AI governance readiness
A fixed-scope review against ISO/IEC 42001 and the NIST AI RMF.
SOC 2 and ISO readiness
Implementation advisory. A licensed CPA firm performs any SOC 2 examination.
Vendor evaluation
RFI/RFP development, due diligence, and a selection you can defend.
Where to Start
Whatever your size or stage, there is a practical first step. Pick the one that sounds like your situation.
Customers, auditors, or your board are asking how you govern AI
The AI Governance Readiness Review: a prioritized view of your AI governance and security posture, with a clear view of what to do first.
A customer, investor, or auditor wants proof your security holds up
Security questionnaires, ISO 27001, NIST CSF, SOC 2 readiness, and AI governance readiness, right-sized to what you need to show.
Choosing a provider?
Vendor evaluation, RFI/RFP development, due diligence, and a selection recommendation you can defend.
Need leadership without the full-time hire?
Fractional CISO, BISO, or program leadership, from a few hours a month to a full retainer.
Private equity firm or portfolio company?
Fractional security leadership, SOC 2 and ISO readiness, vendor selection, and AI governance for portfolio companies, scoped to the hold period and the questions customers and buyers will ask.
Prime contractor or public sector?
A senior-led small-business partner with an active SAM.gov registration, Oregon COBID certified (WBE, MBE, ESB, DBE) and SBA WOSB in process.
Why Verolara
Programs rarely fail for lack of a governance framework. They fail when cybersecurity, operational risk, AI, and delivery leadership operate in isolation. Verolara bridges executive governance and technical execution, across security operations, ISO/NIST readiness, vendor selection, and delivery.
Program builder, not only reviewer
Our founder built an enterprise security program from inception to maturity at Fortune 100 scale. About our founder →
Right-sized to your stage
An enterprise-grade method scaled to your organization's size and risk, from a first review to a retainer.
Independent and vendor-neutral
Advice on tools, platforms, and providers that you can defend to your board, with no products of our own to sell.
AI Governance Readiness Review
Companies are adopting AI faster than they can govern it. This Review closes that gap.
A fixed-scope review against ISO/IEC 42001 and the NIST AI RMF shows where you stand and what to do first. Scope, timeline and fee are agreed in writing before work begins.
SOC 2 and similar examinations are performed by a licensed CPA firm; we provide implementation advisory only.
Frequently asked questions
What is a fractional CISO?
A fractional CISO is a senior security leader who works with your organization part-time instead of as a full-time hire. Engagements range from a few hours a month to a fuller retainer, and every engagement has a stated end state and hand-off plan so your team can run the program afterward.
What is the difference between SOC 2 readiness and a SOC 2 report?
Readiness is the preparation: scoping, closing control gaps, and building evidence. The SOC 2 report is issued by a licensed CPA firm after its examination. Verolara provides implementation advisory only and does not perform the examination or issue the report. Readiness work does not guarantee a particular examination result. The AICPA describes SOC engagements as services that CPAs provide.
What is ISO/IEC 42001?
ISO/IEC 42001 is an international standard that specifies requirements for establishing, implementing, maintaining, and continually improving an AI management system. ISO published it in December 2023. Our AI Governance Readiness Review assesses you against it and the NIST AI RMF. It is an advisory assessment, not a certification.
Is the NIST AI Risk Management Framework mandatory?
No. NIST released AI RMF 1.0 in January 2023 and describes it as intended for voluntary use. Customers, auditors, and insurers increasingly ask about alignment with it, which is why many organizations use it as a common reference point.
How long does an AI Governance Readiness Review take, and how is it priced?
The review has four phases and four deliverables. It is priced by the number of AI systems in scope, and duration depends on the size and complexity of your organization. Scope, timeline, and fee are agreed in writing before work begins.
Do you work with private equity firms and their portfolio companies?
Yes. We support portfolio companies with fractional security leadership, SOC 2 and ISO readiness, vendor selection, and AI governance, scoped to the hold period. See our private equity overview.
Where are you based, and who do you serve?
Verolara is based in Lake Oswego, Oregon (Portland metro). We work with organizations of every size and stage, hybrid in the Portland metro area and remotely worldwide, including enterprises, private equity portfolio companies, prime contractors, and public sector agencies.
Talk it through
A short conversation is usually enough to tell what kind of support fits. No obligation.
Firm Leadership
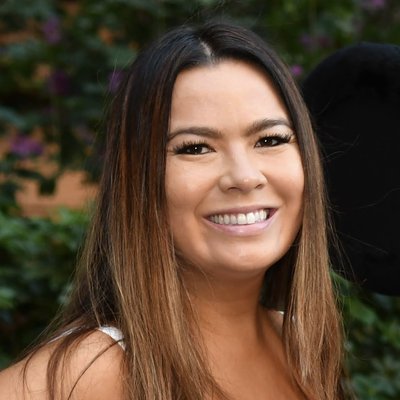
Maria Kimberling Tracy, MBA, CISM, PMP, is the Managing Principal of Verolara, bringing over 20 years of executive program and portfolio leadership across Fortune 100 organizations, including Nike and Albertsons.
Her work centers on building resilient security programs and high-performing executive teams—harmonizing NIST frameworks, ISO standards, and business strategy into one integrated operating model.
Executive Certifications & Credentials
Executive Track Record Highlights
- Helped build Nike's Corporate Information Security organization from inception into a global enterprise practice.
- Senior cybersecurity lead on a major enterprise ERP migration (SAP S/4HANA) at a global retailer.
- Executive Sponsor of Nike's Secure by Design Center of Excellence.
- Replaced a third-party professional services agreement by building risk remediation advisory in-house.
- Built and led a globally distributed team of security advisors with direct budget accountability.
About the Name
Verolara draws on the Latin verus, meaning true, paired with a name that evokes protection. The mark is a Venn diagram: overlapping circles for the services Verolara offers, working as one integrated approach rather than separate efforts. Its V doubles as a checkmark, for verification.
True. Verified. Integrated.
Small Business & Prime Contractor Teaming
Verolara is a woman- and minority-owned small business, certified by the State of Oregon (COBID) as a Woman Business Enterprise (WBE), Minority Business Enterprise (MBE), Emerging Small Business (ESB) and Disadvantaged Business Enterprise (DBE). SBA WOSB certification is in process. It is available as a subcontractor or teaming partner for prime contractors and enterprise clients of any size across transportation and infrastructure, healthcare, higher education, utilities, and financial services, alongside state, local, and federal agencies. Eligible and willing to pursue a security clearance for qualifying engagements. Current registrations and codes:
Certifications & Classification Codes
State and federal small-business status alongside primary NAICS codes for procurement matching.
Privacy Policy
Effective October 13, 2026
Verolara, LLC (“Verolara,” “we”) respects the confidentiality of the people and organizations who contact us. This policy explains what this website collects and how it is used.
What we collect
Only what you choose to send through the contact form or by email: your name, organization, email address, title, the type of help you are looking for, timing, any context you add, and how you heard about us. The form also records which part of this site you came from, such as the Teaming page or the private equity page, so we can respond appropriately.
How we use it
To respond to your inquiry, to prepare for a conversation, and to keep business records of that contact. We do not sell your information, and we do not use it for advertising.
Confidential material
Please do not send sensitive or confidential documents through the contact form. If you have an RFP, RFI, or other material to share, tick the NDA option on the form or email us, and we will send a mutual NDA first and agree a secure way to share the material, including your organization's preferred platform.
Service providers
The site is hosted on Netlify, which also processes form submissions on our behalf. The site loads its typefaces from Google Fonts, which means your browser requests those font files from Google. We use a SAM.gov registration for federal contracting, which is a separate public record.
Cookies and analytics
This site does not use advertising cookies, and we do not run analytics on it at this time. If that changes, we will update this page.
Your choices
You can ask us to correct or delete the information you sent by emailing contact@verolara.com. Where we are legally or contractually required to keep a record, we will tell you.
Security
We use reasonable technical and organizational measures to protect information sent to us, and we limit access to those who need it. No method of transmission over the internet is completely secure, so please keep that in mind when deciding what to send.
Changes and contact
We may update this policy and will change the effective date when we do. Questions: contact@verolara.com.
Start a conversation
Your inquiry goes to a senior advisor, and a mutual NDA is available before you share anything sensitive. Name, organization, and email are all we need. We reply personally, and there is no obligation.
A senior advisor will review it and reply by email. If you asked for a mutual NDA, that comes first. If your matter is time-sensitive, feel free to also connect on LinkedIn.